Understanding Cryptography: From Established Symmetric And Asymmetric Ciphers To Post-quantum Algorithms Springer Nature Link
Protect delicate property with centralized key and certificate management—automate cryptographic controls and strengthen safety throughout your data system. Whereas still in its early phases, quantum encryption has the potential to be far more secure than previous forms of cryptographic algorithms and, theoretically, even unhackable. While modern computer systems retailer information utilizing a binary format referred to as a “bit” during which a “1” or a “zero” may be stored; a quantum pc stores knowledge using a quantum superposition of multiple states.
Cryptography Hash Functions
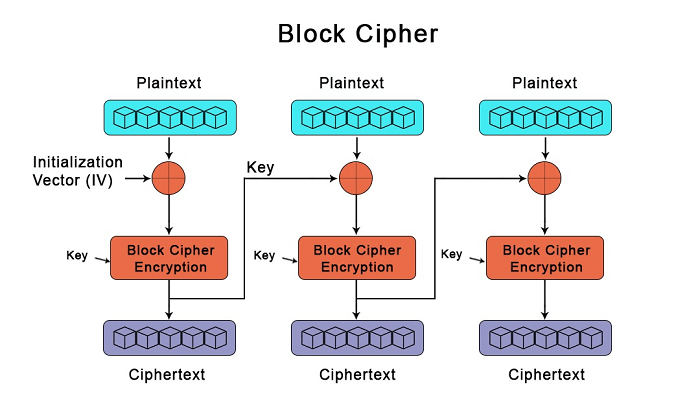
In the subsequent sections, we will first talk about the mannequin of block cipher adopted by DES and AES, two of essentially the most influential fashionable block ciphers. Monoalphabetic cipher is a substitution cipher in which for a given key, the cipher alphabet for each plain alphabet is fixed all through the encryption process. For example, if A is encrypted as D, for any variety of incidence in that plaintext, A will at all times get encrypted to D. For this type of scheme, each sender and receiver agree on a secret shift number for shifting the alphabet. This number which is between zero and 25 turns into the necessary thing of encryption.
Desk 2 presents a mapping of key 5G/B5G attack vectors to the corresponding cryptographic countermeasures in our proposed AES-DES-RSA hybrid framework. The model effectively mitigates threats such as MITM, rogue base stations, slicing breaches, DDoS assaults, brute-force cryptanalysis, and quantum threats. In addition, it outlines potential future enhancements including post-quantum cryptography (e.g., CRYSTALS-Kyber) and AI-driven anomaly detection for adaptive safety in evolving 5G environments.
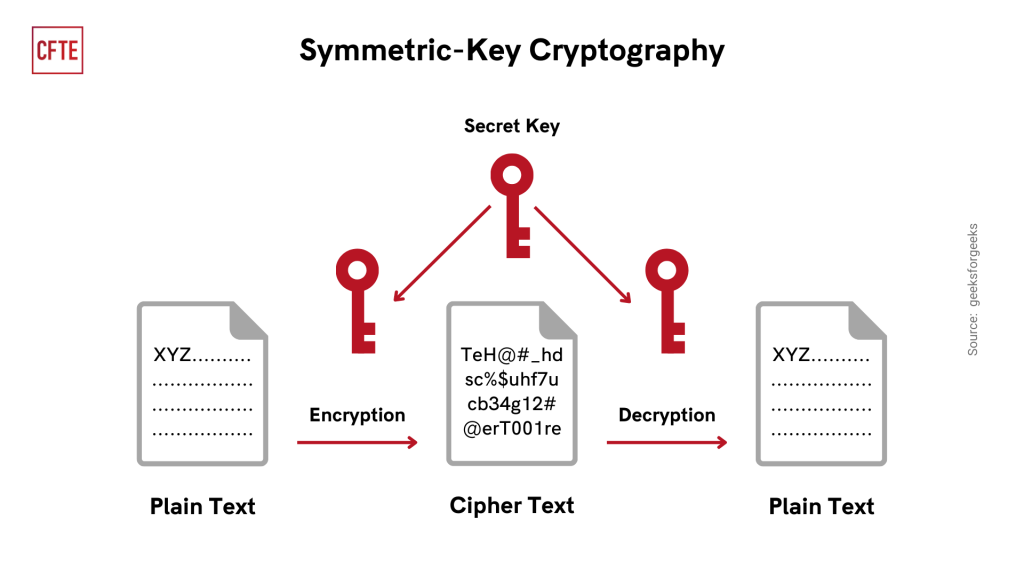
- Algorithms such because the Superior Encryption Commonplace (AES) and Knowledge Encryption Standard(DES) are symmetric methods.
- In this way, symmetrical cryptosystems require every party to have access to the secret key earlier than the encrypting, sending and decrypting of any information.
- AES makes use of 10 rounds for 128-bit keys, 12 rounds for 192-bit keys and 14 rounds for 256-bit keys.
- Non-repudiation ensures that a sender cannot deny sending a message or signing a document.
- This part explains the basics of securing info and the fundamental elements of cryptographic systems.
Right Here https://carrating.org/blog/2014-volvo-v60-is-their-most-powerful-wagon-ever is a jumbled Ciphertext alphabet, where the order of the ciphertext letters is a key. In case of proprietary algorithms, security is ensured via obscurity. Non-public algorithms will not be the strongest algorithms as they’re developed in-house and may not be extensively investigated for weak spot. Keeping the algorithms secret might act as a big barrier to cryptanalysis.
Asymmetric Key Cryptography
Cryptographers need to sustain with the ever-evolving world of cyberthreats, thus they must often refresh their data. The obligations of their career also can vary daily, adding to its dynamic nature. The job may be troublesome at times as a outcome of significance of protecting delicate digital data, as errors can lead to breaches of privacy. To allow you to make a good move concerning this profession, consider the advantages and drawbacks of being a cryptographer. Cryptography is very important on this trendy world because it helps to guard your digital stuff from hackers by turning information into secret language or code. Ciphers are strategies used to remodel readable knowledge (plaintext) into unreadable data (ciphertext) in order that only approved events can perceive the unique content.
Commonly Used Uneven Algorithms
Like RSA, it depends on amathematical downside, the discrete logarithm drawback, for which noefficient answer has been discovered, and requires keys of no much less than 1024bits. RC5, RC6, Camellia, ARIA, IDEA, Serpent, AES, ChaCha20, CAST, Twofish, and CAST are a quantity of in style symmetric encryption algorithms. All of these methods are thought of as safe when correctly configured and utilized. To repair this, encryption algorithms will either ask you to cross in a random “initialization vector”or not-necessarily-random however unique “nonce” worth. In either case, the encryption algorithm will use theseinputs to alter the encryption process so that the identical plaintext data will encrypt to different values even withthe same key. Each the sender and receiver have to know the key (3) to encrypt and decrypt messages with the help of Caesar Cipher algorithm.

Imagine that you’ve got a secret message, and you solely need sure people to crack the code. It is like maintaining your message into an unseen envelope that solely the designated receiver can open. Cryptography is the science of protecting data using mathematical techniques to make sure https://carrating.org/technology/hybrid-innovations-new-approaches-for-boosting-efficiency confidentiality, integrity, and authentication. It transforms readable data into unreadable form, stopping unauthorized access and tampering. Such methods were used earlier than trendy computer systems., primarily use substitution and transposition methods to cover the original message.